Showing posts with label fudcrypt. Show all posts

Friday, October 4, 2019

Fudcrypt using H-Worm from WSH RAT


Fudcrypt builder, like WSH RAT builder uses HWorm. The last version of the builder from 24th of September provides some interesting insight:


In the case of Fudcrypt, compared with WSHRAT, the HWorm payload, in VBS, is not included as a resource, but is pull from a remote URL. This payload is then obfuscated with a routine. The code of the routing is below:


The interesting part is that the plain text payload (HWorm) contains  "live:unknown.sales64". Unknown.sales64 is the actor behind WSHRAT and the skype ID is always in the header of the HWorm in VBS and JS.


The User-agent is also "WSHRAT" .

In terms of the code and functionality of the HWorm used by Fudcrypt, is not the latest version used in WSH RAT. It is possible Fudcrypt actors don't have access to the latest version of the WSHRat where the newer code is used


With Fudcrypt it is also possible to 'crypt' Java files. In order to do that, the builder contains the full Java JRE environment:


The code to create and 'crypts' the  Java code works in a similar way than the VBS.


Monday, September 2, 2019

WSH RAT and the link to unknowcrypter and Fudcrypt

There are plenty of malspam campaigns using the the code "MT103" from SWIFT to claim some kind of payments. 


However, recently there was one in particular using some malicious JavaScript as an attachment quite interesting. Some samples of the campaign can be found here and here 

The payload in those campaigns delivered the malware "wsh RAT".  This malware family is quite new, however the actor behind is not new at all, but linked to some other crypters services mentioned in this blog.


Analysis of the code - overlap with Uknowncrypter and Fudcrypt

While I did the analyses of the sample here I found several interesting points which I will detail here.

The obfuscation mechanism used is very similar in terms of the 'algorithm' and base64 encoding to the one used in unknowcrypter and Fudcrypter 


The final decoded payload leads to some interesting indicators.


This code is similar  Vjw0rm  which is used by unknowcrypter. Also, the host "unknownsoft.duckdns[.]org" was used by uknowncrypter at some point.  
But the most interesting aspect is the skype ID "unknown.sales64"
The skype ID is linked to the domain http[:]//www.wshsoftware[.]site where WSH RAT is sold.


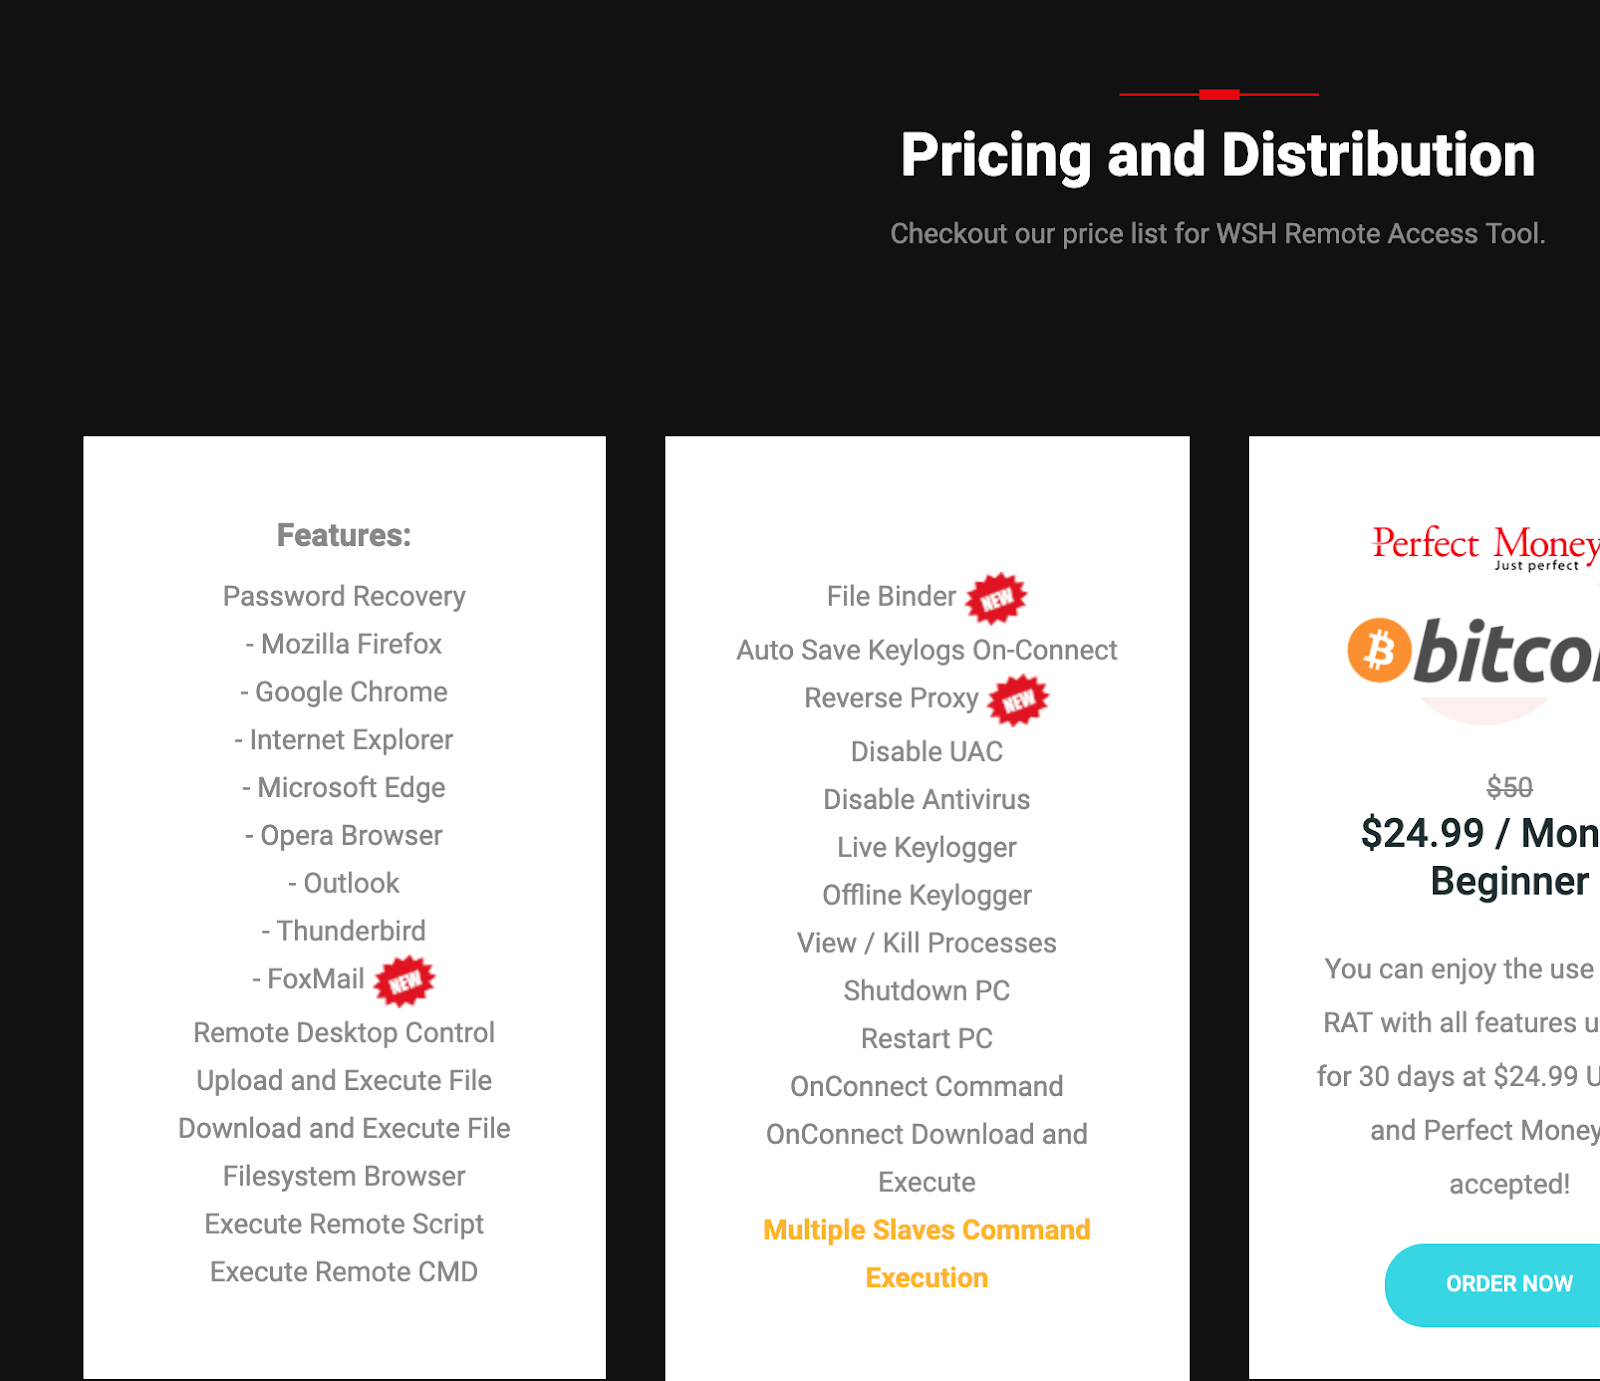
The capabilities of this RAT are described in the website:


A full video of the capabilities of this RAT is also linked in the main website

https://youtu.be/rdG16vk9qNQ

According to the video and some screenshots the malicious payload can be generated in VBS and JS


Unknowcrypter generates JavaScript code while Fudcrypt VBS code, however the code in essence was the same in both cases, as showed in the post here 

The domain wshsoftware[.]site has been registered with the email address stonexevans@gmail[.]com


This same email address was used to register the domain "fudcrypt[.]com" which was used to sell Fudcrypt service at some point


So "WSH RAT", "unknowcrypter" and "Fudcrypt" are linked between them


In the next blog I will dig into the code and capabilities of the malware